Set the rule
Dry-run a policy, observe it in Shadow mode, then promote a reviewed version to Active.
Flightdeck is the control plane for DVARA Enterprise. Manage policies, review recorded spend, and investigate the evidence DVARA produces on governed traffic.
Traffic stays on the gateways. Flightdeck manages configuration and displays recorded activity.
Dry-run a policy, observe it in Shadow mode, then promote a reviewed version to Active.
Filter recorded activity, costs, and gateway metrics by the scope your team needs.
Inspect supported signing details and export matching audit events for review.
This demo policy denies a retired model. The dry run returns DENIED and explains why without calling a provider.
Use Shadow mode to observe a policy without letting it block traffic, then promote it to Active. Changes have version history and rollback. Test real gateway requests separately before production.
Follow the policy workflow →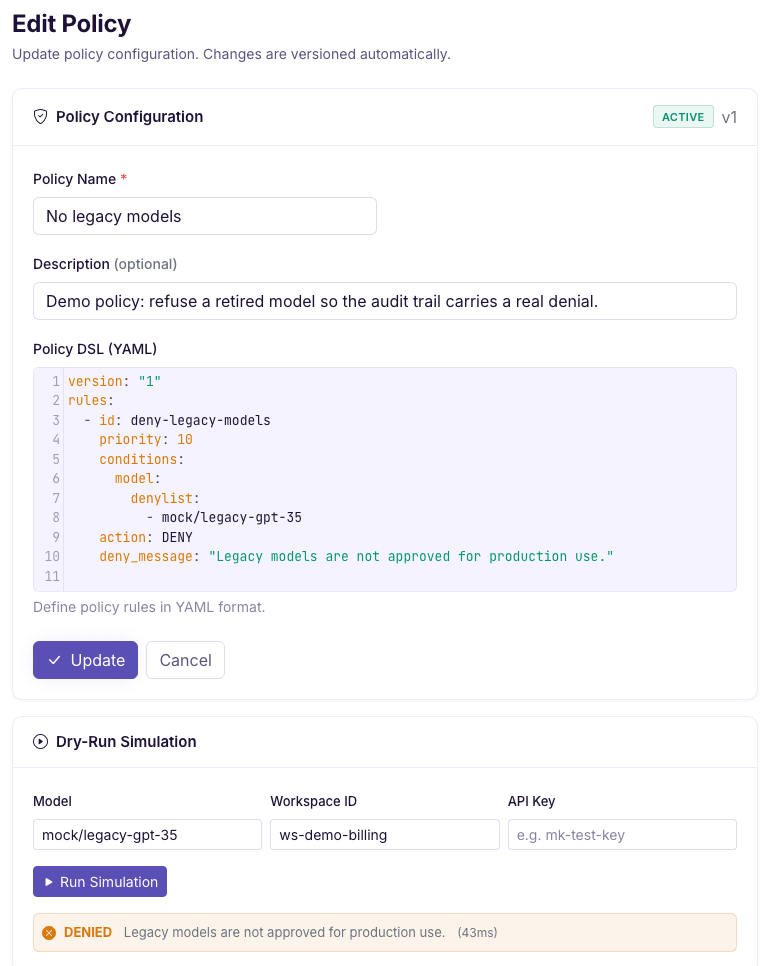
Use recorded metrics and cost history to understand a workspace before you change a route, budget, or policy.
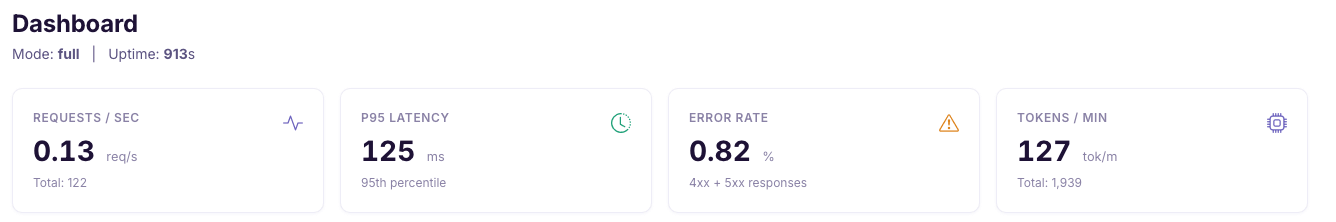
Filter recorded costs by workspace, model, provider, and time. This isolated demo breaks sample history down by provider and model.
Live dashboard metrics need a reachable gateway. Cost and audit views need persisted records.
Review costs and budgets →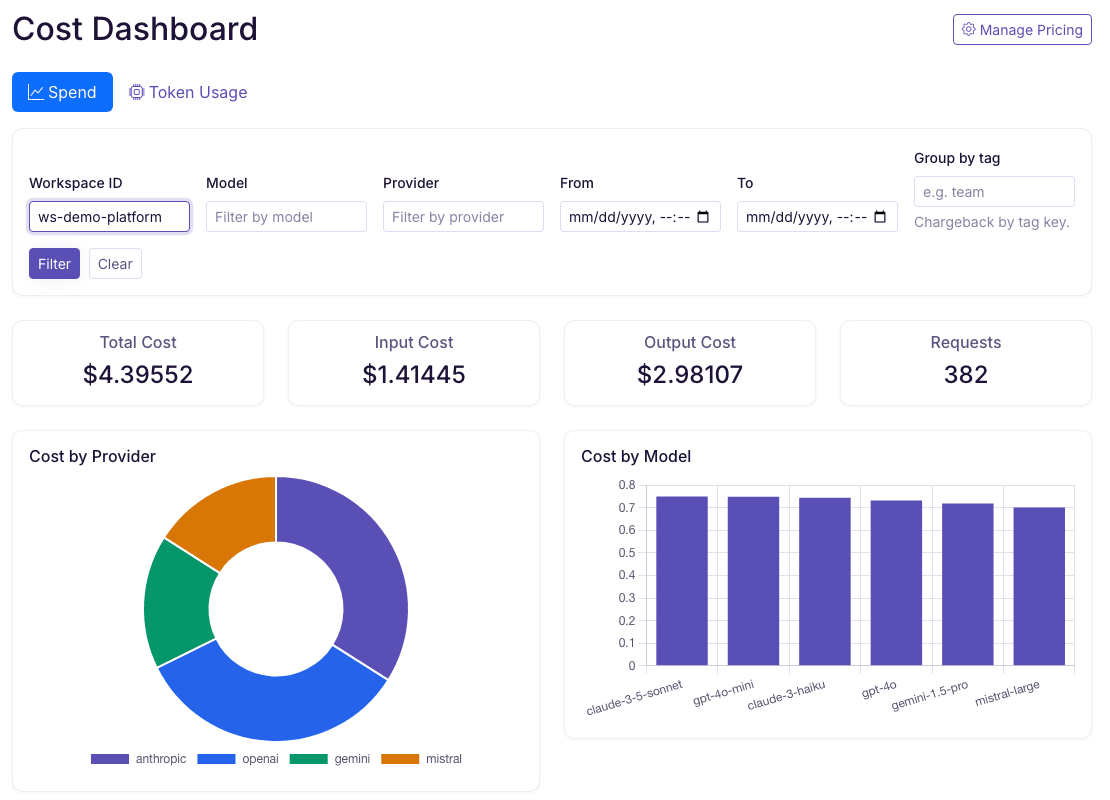
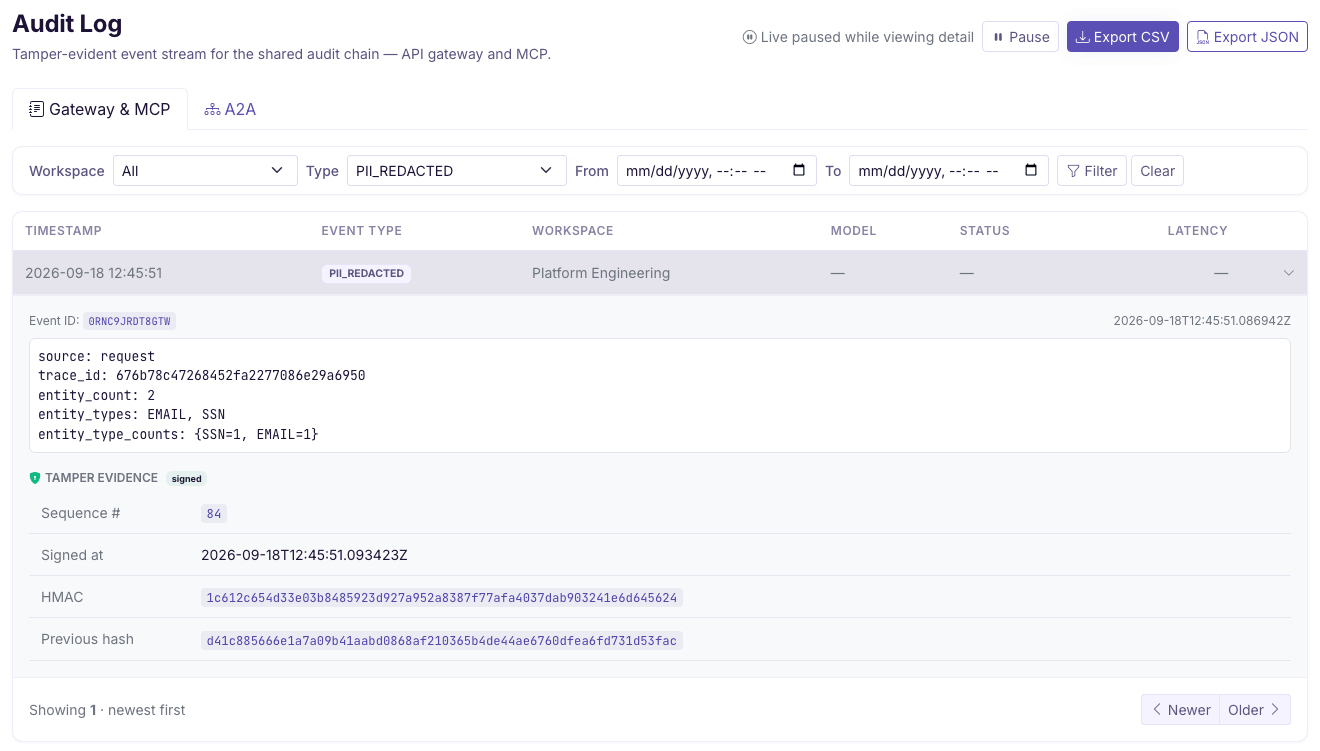
Filter recorded events by workspace, event type, or time. Open a supported event to inspect its control outcome and signing evidence, then export matching records for review.
Signing and hash chaining make supported records tamper-evident; they do not guarantee completeness or create a compliance certification.
Understand audit evidence →No. Flightdeck is part of the Enterprise platform. DVARA Open Source uses file-based configuration and does not include this interface. Pricing explains production and activation terms.
No. The gateways handle traffic and enforce configured controls. Flightdeck manages configuration and displays recorded activity. Direct calls to providers or tools that bypass DVARA are not visible here.
No. The policy dry run evaluates the supplied policy against a sample request without calling a model provider. Test real gateway requests separately before relying on a policy in production.
No. Signing and hash chaining make supported audit records tamper-evident; they do not guarantee that every event was stored. Storage failures can leave gaps. An exported record is evidence to review, not a compliance certification.