01Model call
Clinical documentation
Apply configured PHI handling before the prompt reaches a model.
DVARA is an AI gateway that governs model, tool and agent-to-agent calls in healthcare workflows. Configure PHI handling, tool access, approvals and evidence across one governed request path.
Deploy in your cloud, VPC or on-premises environment. DVARA governs calls routed through it.
Choose log, block, redact or supported tokenization behavior.
Apply access rules, approvals and loop controls to governed calls.
Investigate recorded decisions and supported signing details.
Clinical AI can read context, call operational systems and hand work to another agent. Each call needs a boundary your team can explain.
Apply configured PHI handling before the prompt reaches a model.
Control which MCP tools the agent can reach and which actions wait for approval.
Set rules for A2A calls and limit repeated or cyclic behavior within a session.
PII detection is enabled by default, but the default action is LOG. Detected content continues unchanged. For a healthcare path that must remove or refuse PHI, configure REDACT or BLOCK and test the exact request shapes your agents send.
Compare PII actions and defaults →Summarize the visit for Maria Patel, DOB 04/12/1978, MRN 842791.
Summarize the visit for [REDACTED_NAME], DOB [REDACTED_DOB], MRN [REDACTED_ID].
Register tool servers, expose only the tools a workspace needs, and require a person’s approval for configured high-impact actions. No decision within 300 seconds denies the call by default.
Explore tool governance →Set source, target and skill rules for governed handoffs. Session-scoped loop detection is available when callers send a session ID; repeated calls and cycles can terminate the session by default.
Explore agent-to-agent governance →DVARA does not orchestrate the workflow. Your application or agent framework chooses the tool or peer; DVARA evaluates the call sent through it.
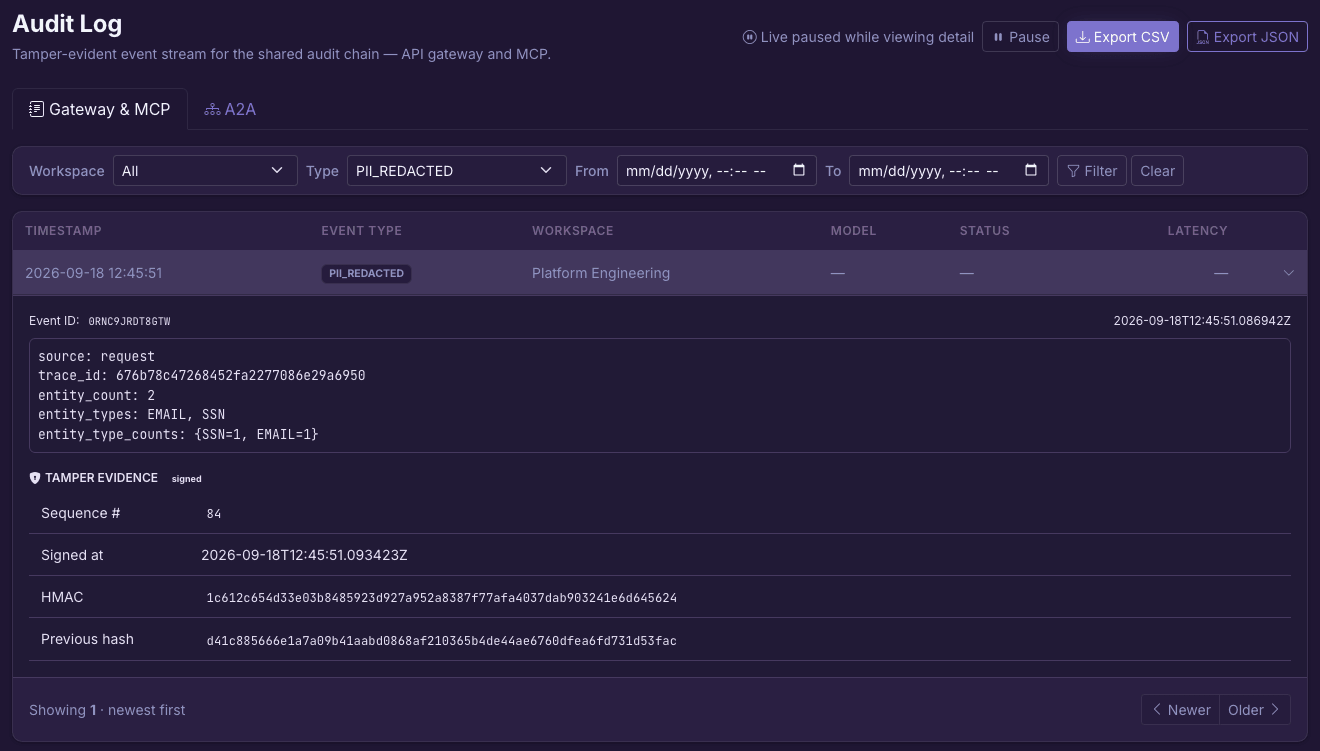
With audit persistence configured, review recorded decisions by workspace, event type and time. Supported HMAC signatures and hash chaining make changes, deletions and breaks detectable during verification.
That evidence is tamper-evident, not immutable, and does not prove that every event was written.
Understand audit evidence →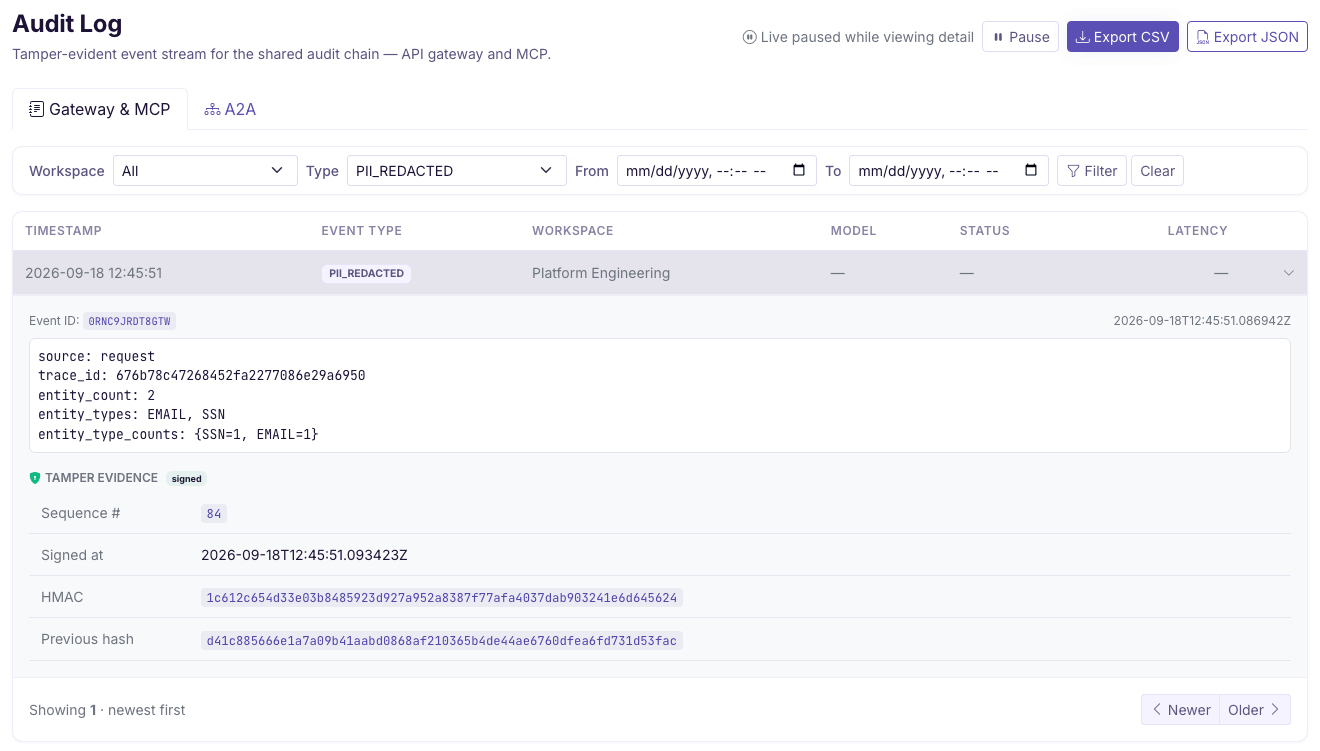
HealthYoda places DVARA in front of its healthcare agents and configured models for PHI redaction, controlled caching and recorded evidence.
Read the HealthYoda story →DVARA can enforce configured PHI actions and record governed decisions. Your compliance program still owns deployment, identity and access, retention, network boundaries, vendor agreements, incident response and operating procedures.
Review deployment options →No. DVARA provides configurable controls that can support a HIPAA compliance program. Deployment, access controls, data handling, business associate agreements, retention and operating procedures remain part of the organization’s responsibility.
No. PII detection logs by default and leaves detected content unchanged. Configure REDACT or BLOCK explicitly, choose detectors that match your data, and test request, response and streaming behavior before production.
Yes. DVARA governs traffic routed through its gateways. Use network restrictions, provider controls and upstream access policy when every call must use the governed path.
Map its model, tool and agent calls, then identify the controls and evidence your team needs for a focused pilot.
Book a healthcare AI session